


CrowdSec is an open-source and participative security solution offering crowdsourced server detection and protection against malicious IPs. Detect and block with our Security Engine, contribute to the network, and enjoy our real-time community blocklist.

CrowdSec Security Engine is an all-in-one IDS/IPS and WAF.
It detects bad behaviors by analyzing log sources and HTTP requests, and allows active remediation thanks to the Remediation Components.
Detection rules are available on our hub under MIT license.
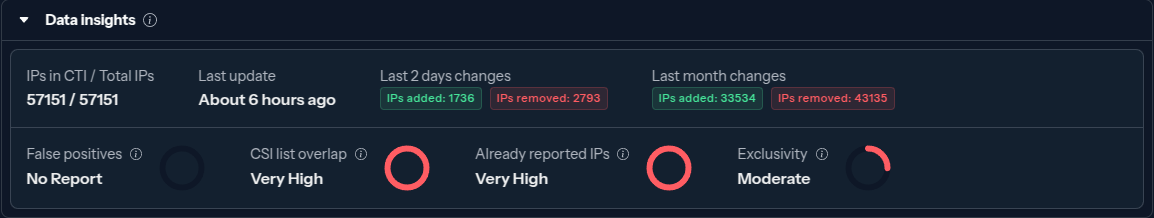
The "Community Blocklist" is a curated list of IP addresses identified as malicious by CrowdSec. The Security Engine proactively blocks the IP addresses of this blocklist, preventing malevolent IPs from reaching your systems.
To fail2ban — CrowdSec reads the same log files and bans the same IPs, but detection and remediation are decoupled: parse logs on one machine, block at the firewall, reverse proxy or CDN on another. Attacks you report feed a community blocklist, so an IP that hits one user gets blocked for everyone else before it reaches them.
To ModSecurity, Coraza and naxsi — the AppSec component is a WAF built on Coraza, so SecLang rules and the OWASP Core Rule Set load as-is. On top of that it adds a YAML rule format, and shares the IP reputation and remediation layer with the log-based engine.
Bot and scraper detection — AppSec can answer a suspicious request with a JavaScript proof-of-work challenge at a tunable difficulty, which stops headless browsers and scrapers while letting verified crawlers such as Googlebot through.
By sharing the threat they faced, all users are protecting each other (hence the name Crowd-Security). Crowdsec is designed for modern infrastructures, with its "Detect Here, Remedy There" approach, letting you analyze logs coming from several sources in one place and block threats at various levels (applicative, system, infrastructural) of your stack.
CrowdSec ships by default with scenarios (brute force, port scan, web scan, etc.) adapted for most contexts, but you can easily extend it by picking more of them from the HUB. It is also easy to adapt an existing one or create one yourself.
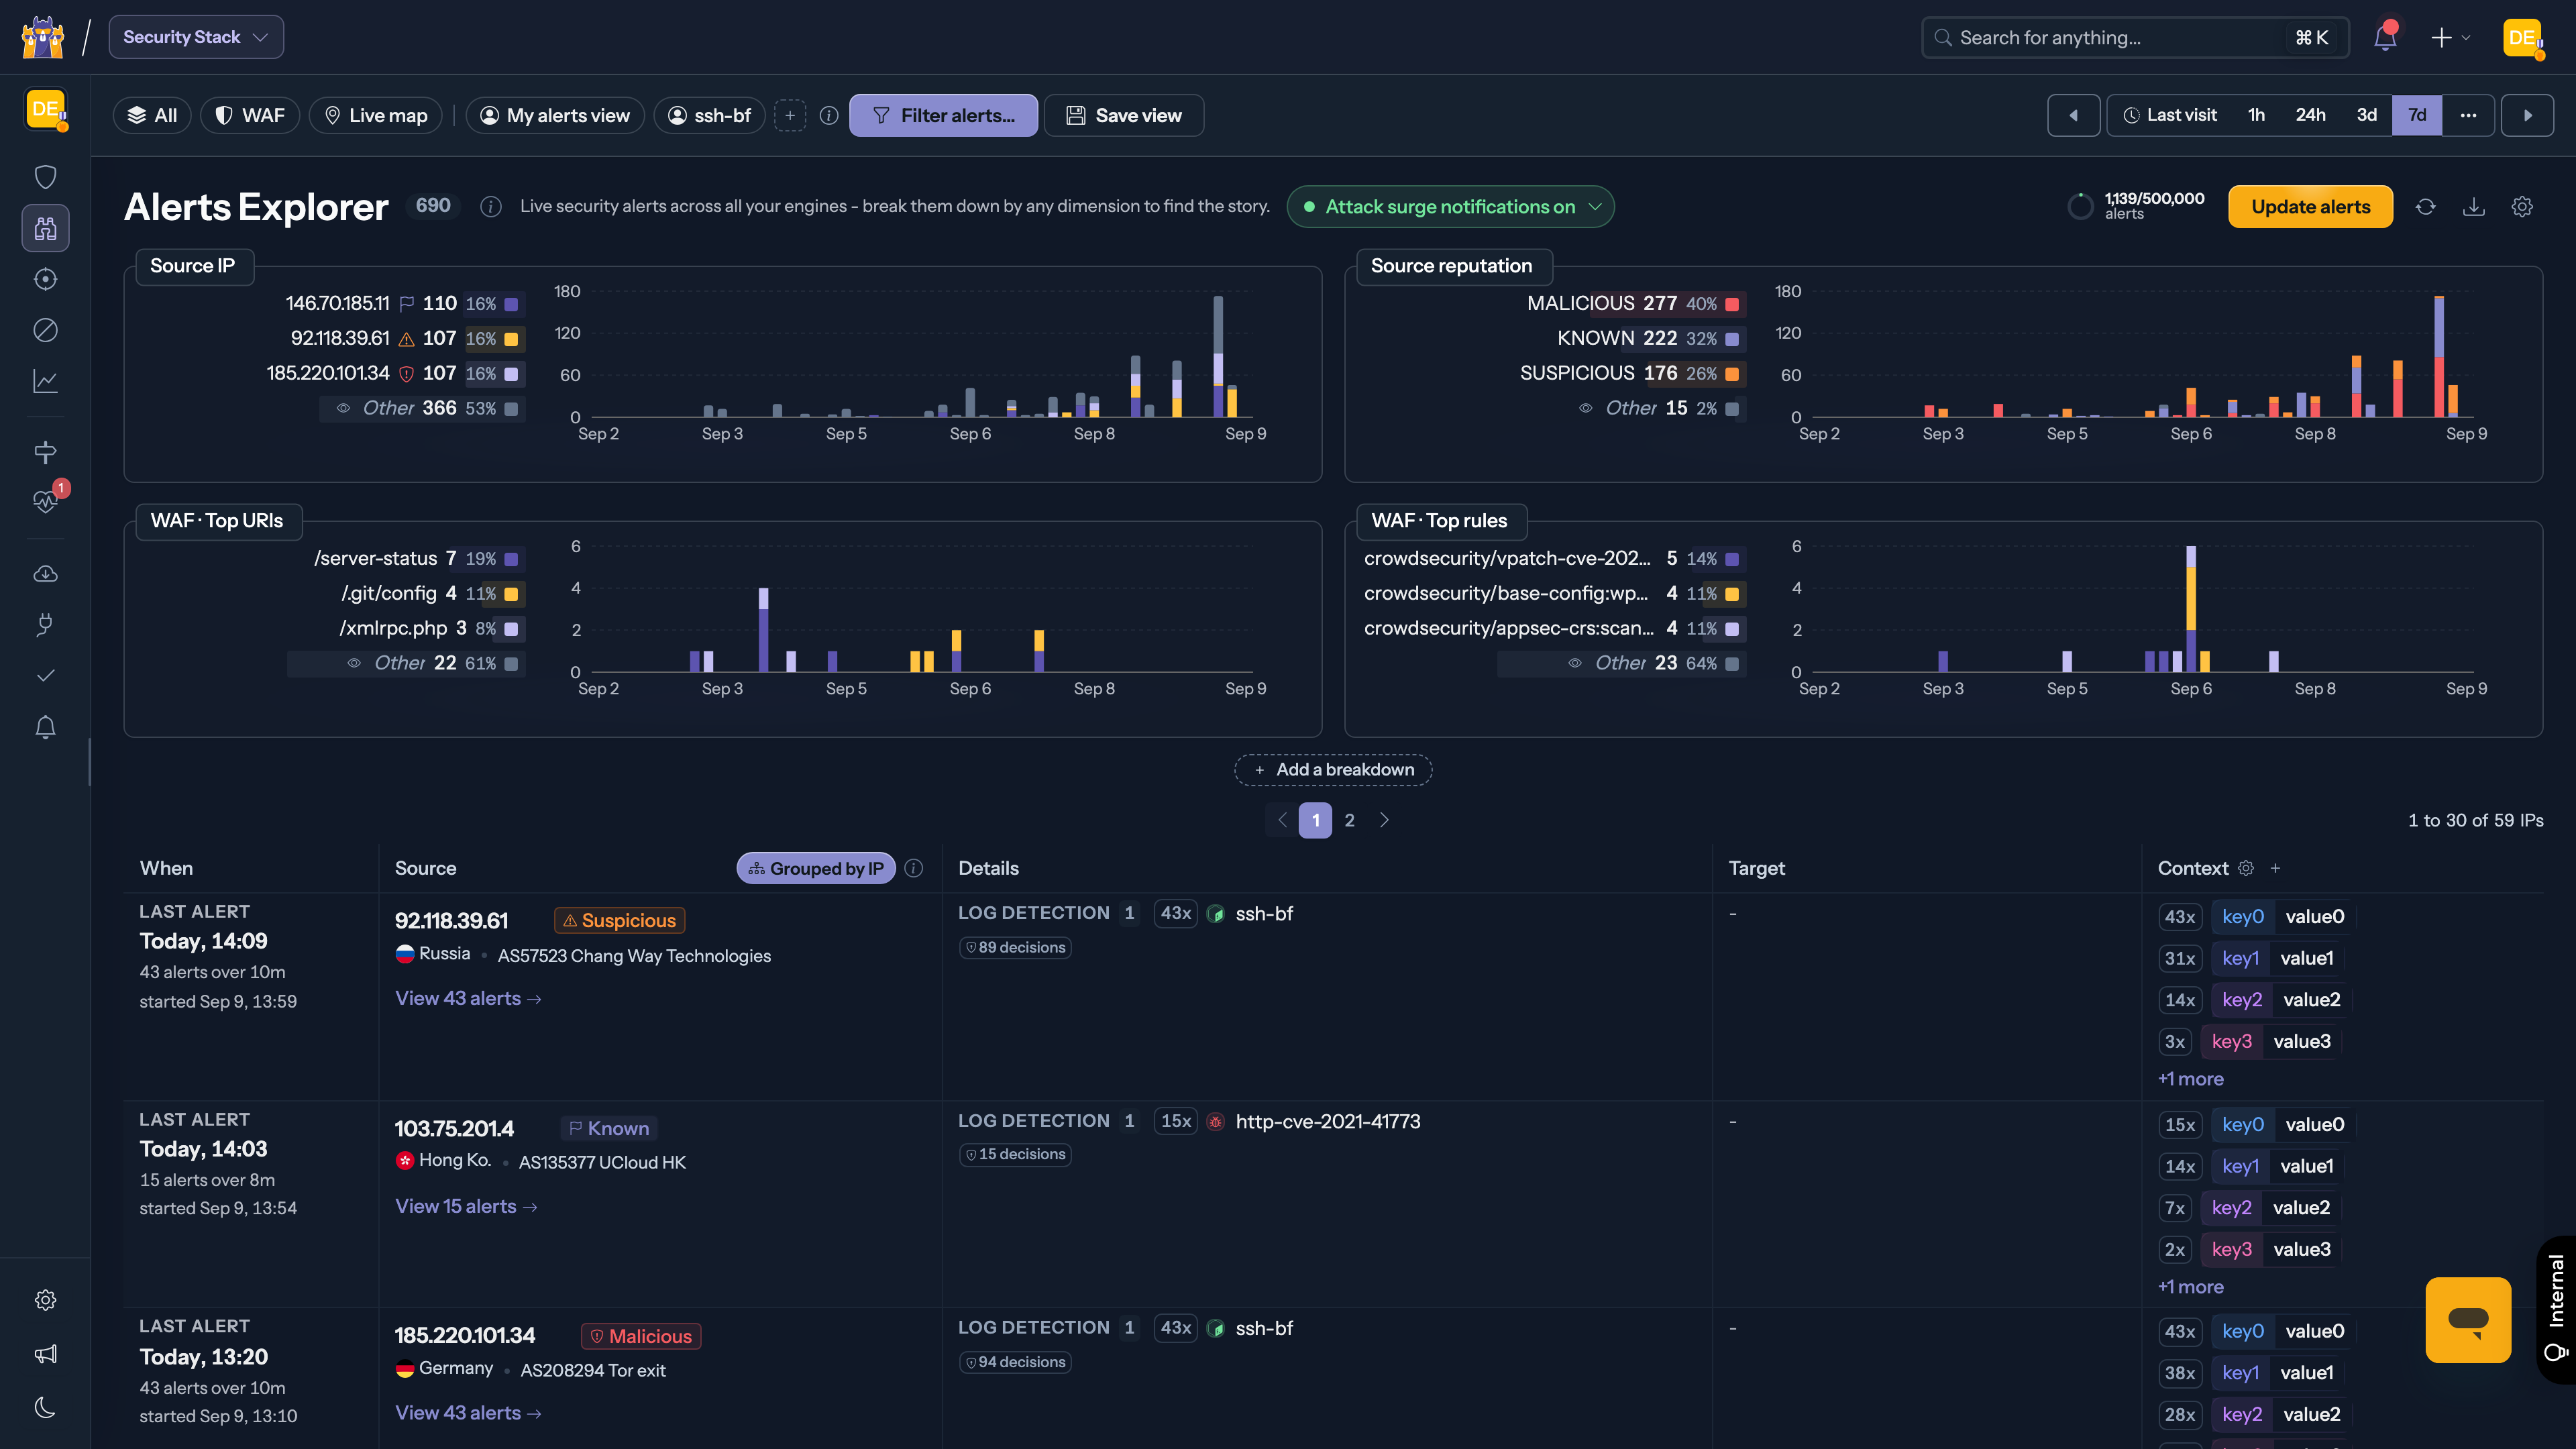
- Console: Supercharge your CrowdSec setup with visualization, management capabilities, extra blocklists and premium features.
- Documentation: Learn how to exploit your CrowdSec setup to deter more attacks.
- Discord: A question or a suggestion? This is the place.
- Hub: Improve your stack protection, find the relevant remediation components for your infrastructure.
- Public Roadmap: Vote for your favorite features and submit ideas to influence what we build next.
- CrowdSec Academy: Learn and grow with our courses.
- Corporate Website: For everything else.
